Pentests that prove every finding.
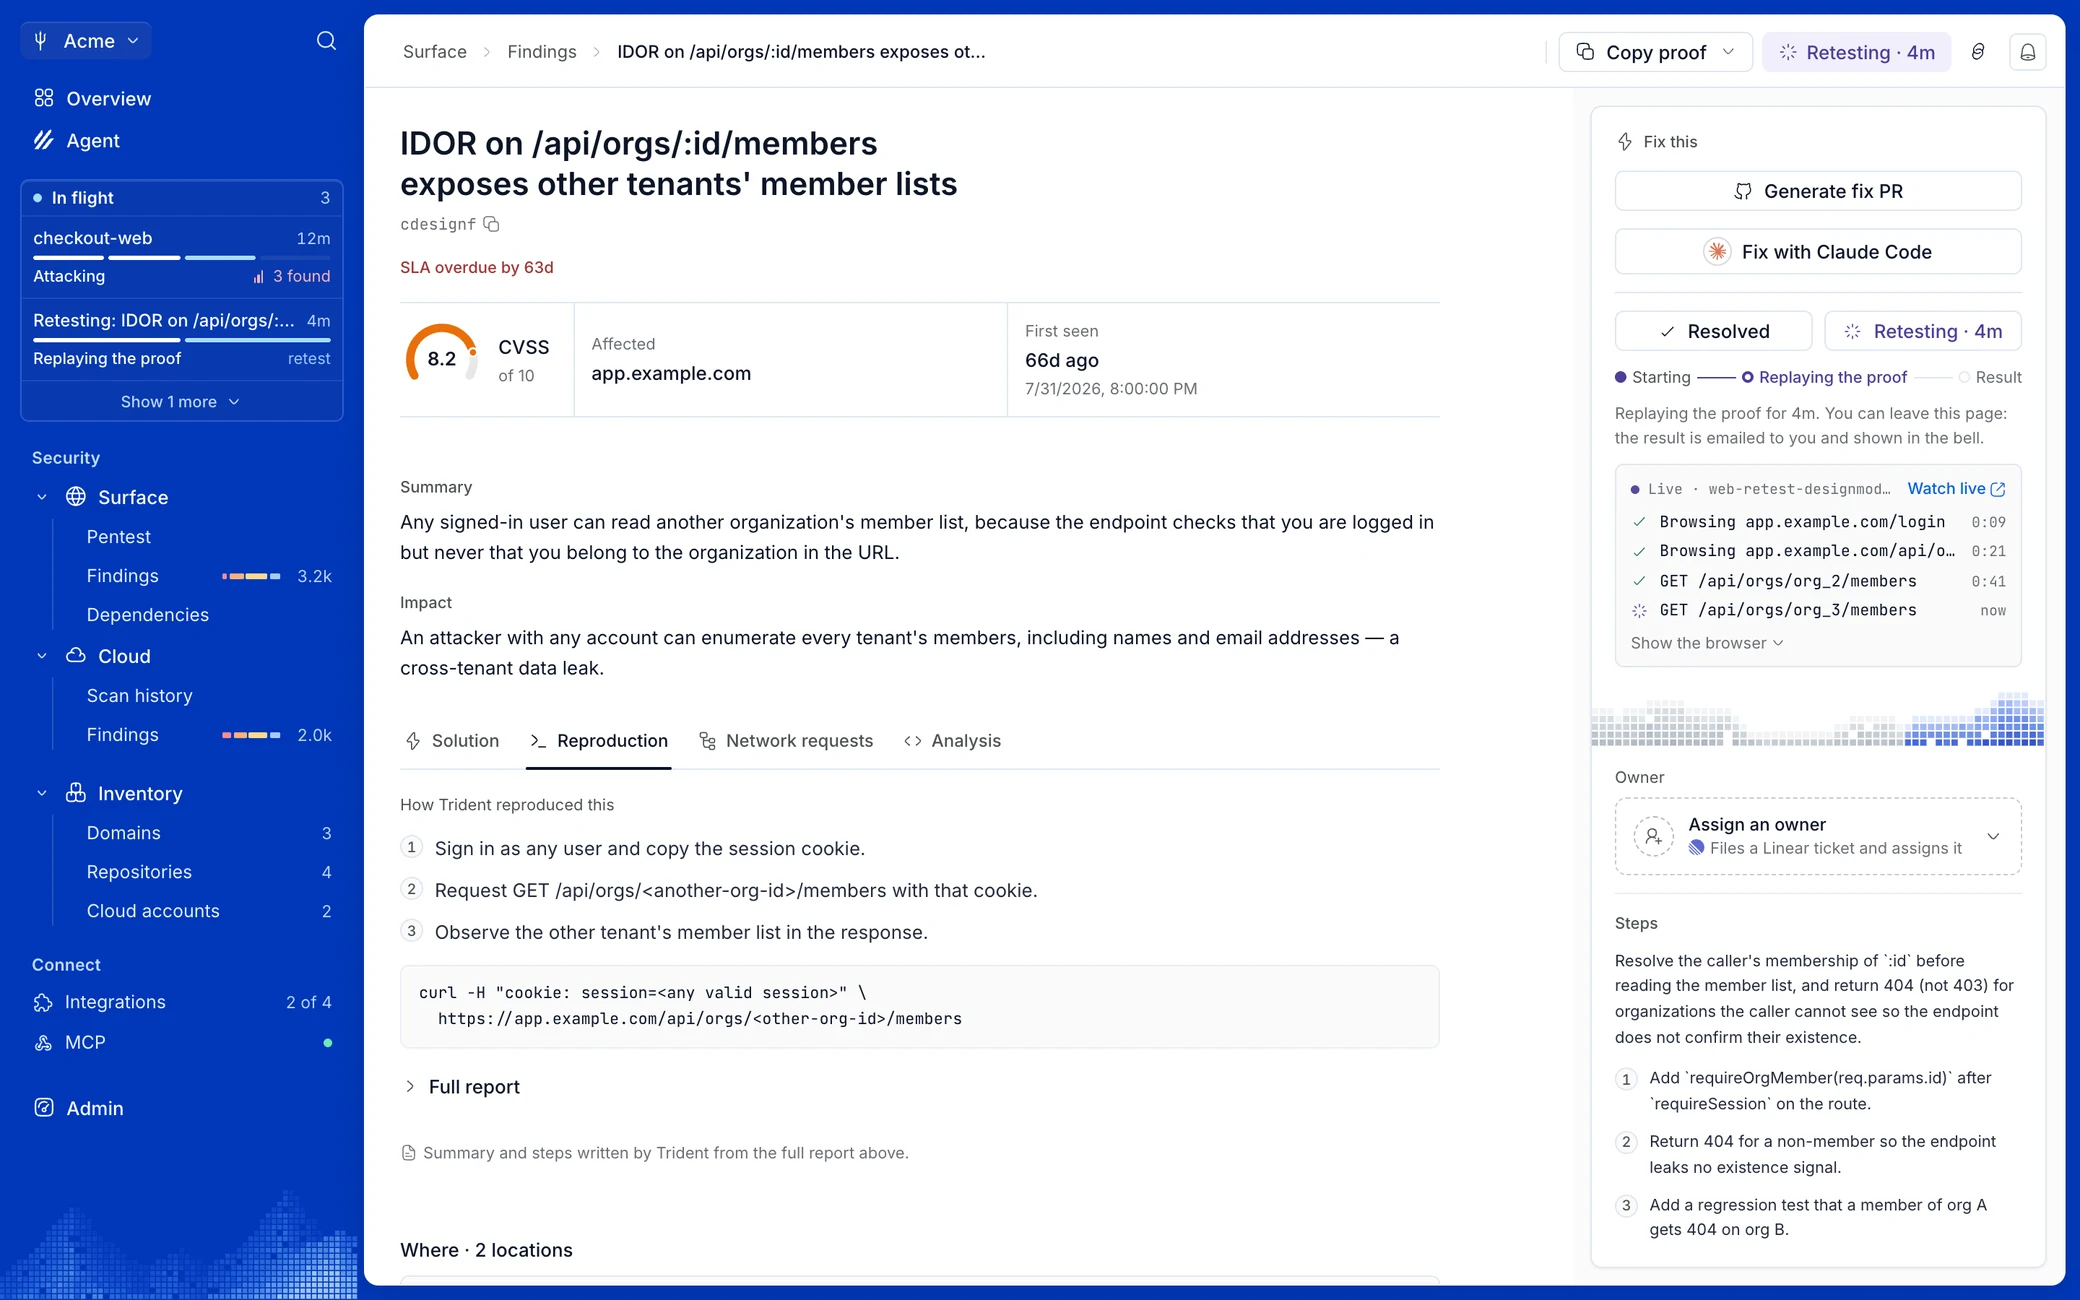
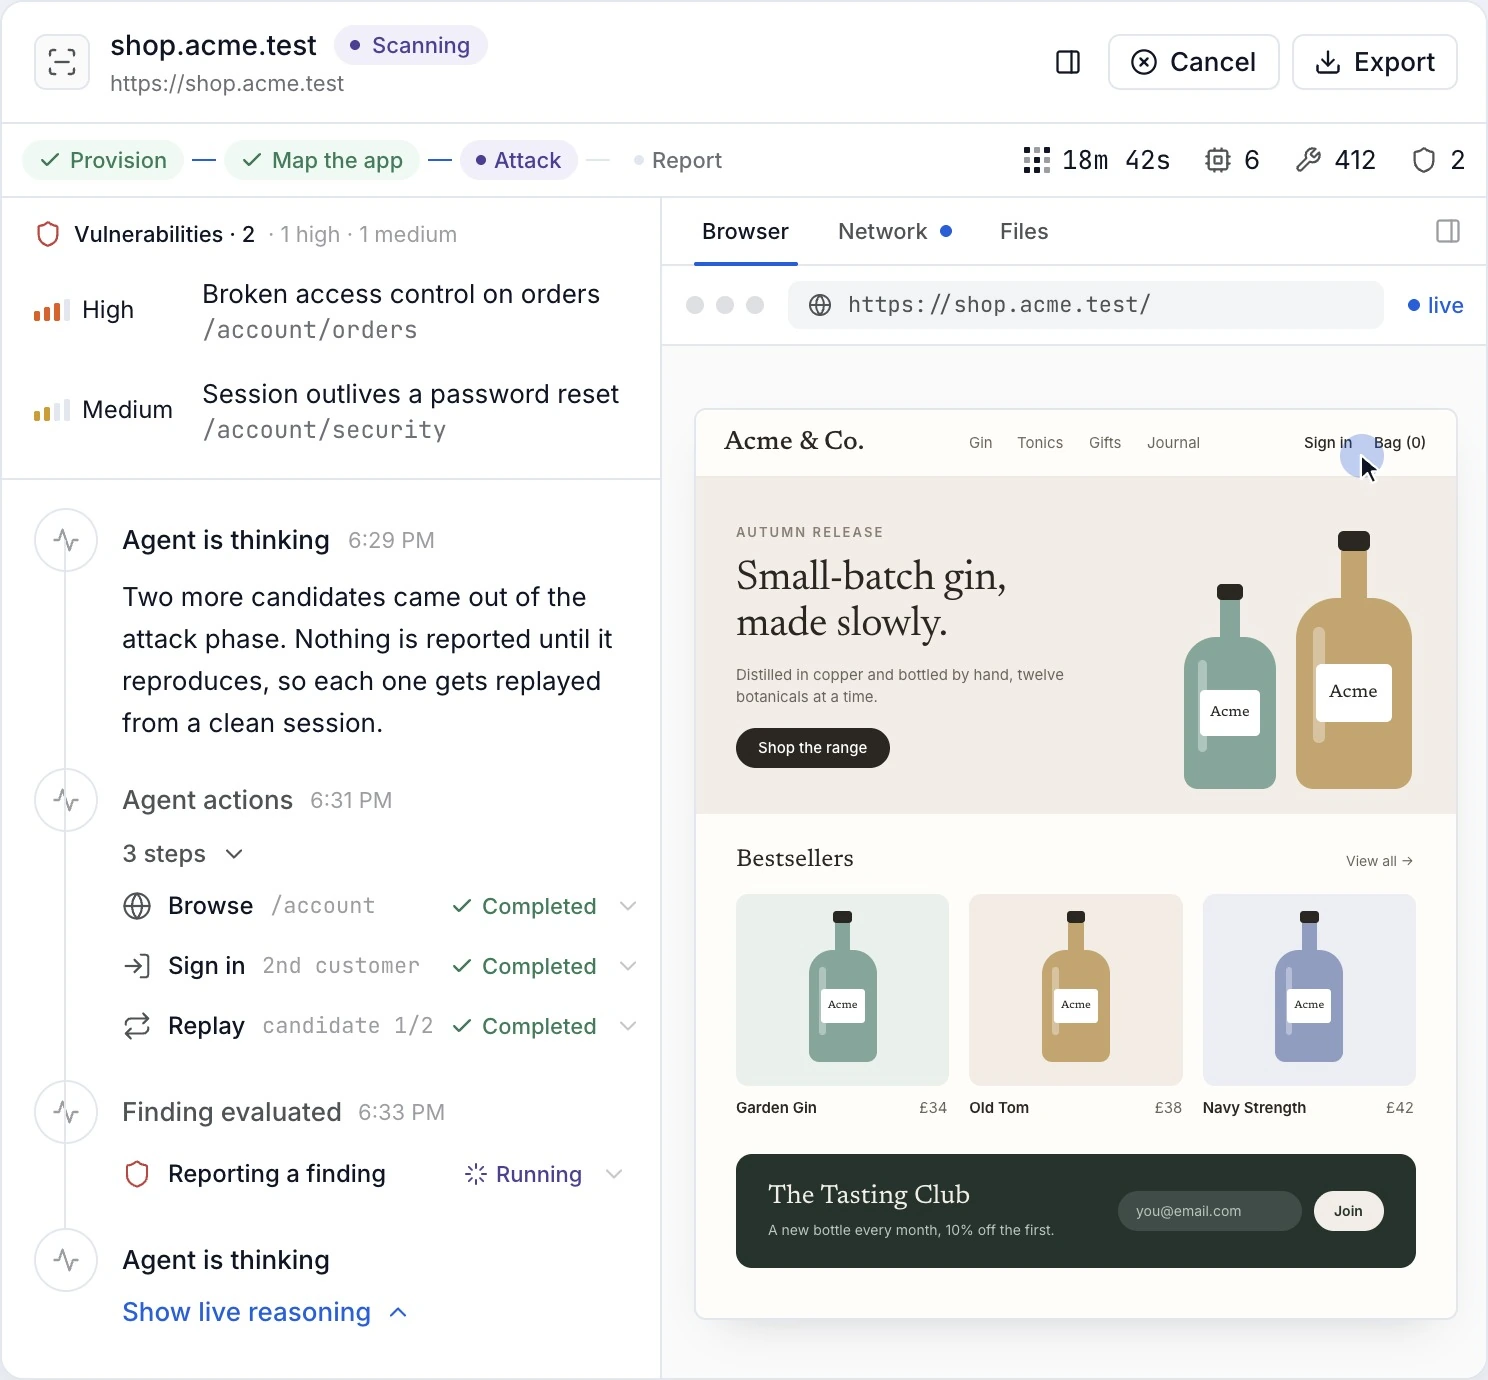
Trident runs the attack instead of guessing at it. Agents map the app, try each idea against it, and replay every candidate from a clean session. Only what reproduces becomes a finding.
The Trident security platform pentests your apps and APIs with AI agents, on a schedule you set. It maps attack paths across AWS, Azure, GCP and Kubernetes and reviews every pull request on GitHub. Every pentest finding ships with its proof of concept.

Trusted by teams shipping fast
Trident runs the attack instead of guessing at it. Agents map the app, try each idea against it, and replay every candidate from a clean session. Only what reproduces becomes a finding.

trident-sentinel reads every change as the PR opens and on each push, flags the exact lines with a fix to commit, and can hold the merge until it is fixed.
Your coding agent pulls a finding over MCP, proof of concept included, and patches it where you already write code.
Tag @Trident in any channel and it answers in the thread from your live findings, scans and PR reviews.
Four soundings we take on every account, from the surface to the seabed.
Read-only, in minutes. Trident maps everything it can reach before the first probe goes out.
See every integration
pkgconf’s --env option wraps every value it prints in single quotes and then puts unescaped, attacker-influenced data between them. Three primitives escalate from a hostile .pc file, through an escaping routine written for the wrong shell context, to command execution driven by a directory name alone.

A few percent of disagreement between two contracts can freeze every deposit and withdrawal in a live crypto vault — and this one went unnoticed for six weeks.

An unauthenticated SSRF in Cisco Unified CM’s WebDialer chains to a JSP webshell and root-level compromise of enterprise voice infrastructure. Cisco patched it on June 3; within weeks attackers were dropping webshells over Tor, and CISA gave federal agencies until June 28 to fix it.
Start a free trial. Your first verified findings land within a day of connecting.
The Trident security platform pentests your apps and APIs with AI agents, on a schedule you set. It maps attack paths across AWS, Azure, GCP and Kubernetes and reviews every pull request on GitHub. Every pentest finding ships with its proof of concept.

Trident runs the attack instead of guessing at it. Agents map the app, try each idea against it, and replay every candidate from a clean session. Only what reproduces becomes a finding.
trident-sentinel reads every change as the PR opens and on each push, flags the exact lines with a fix to commit, and can hold the merge until it is fixed.
Your coding agent pulls a finding over MCP, proof of concept included, and patches it where you already write code.
Tag @Trident in any channel and it answers in the thread from your live findings, scans and PR reviews.