New researchA pristine file, a directory name, and arbitrary code
Continuous security testing,with proof attached.

The Trident security platform pentests your apps and APIs with AI agents, on a schedule you set. It maps attack paths across AWS, Azure, GCP and Kubernetes and reviews every pull request on GitHub. Every pentest finding ships with its proof of concept.

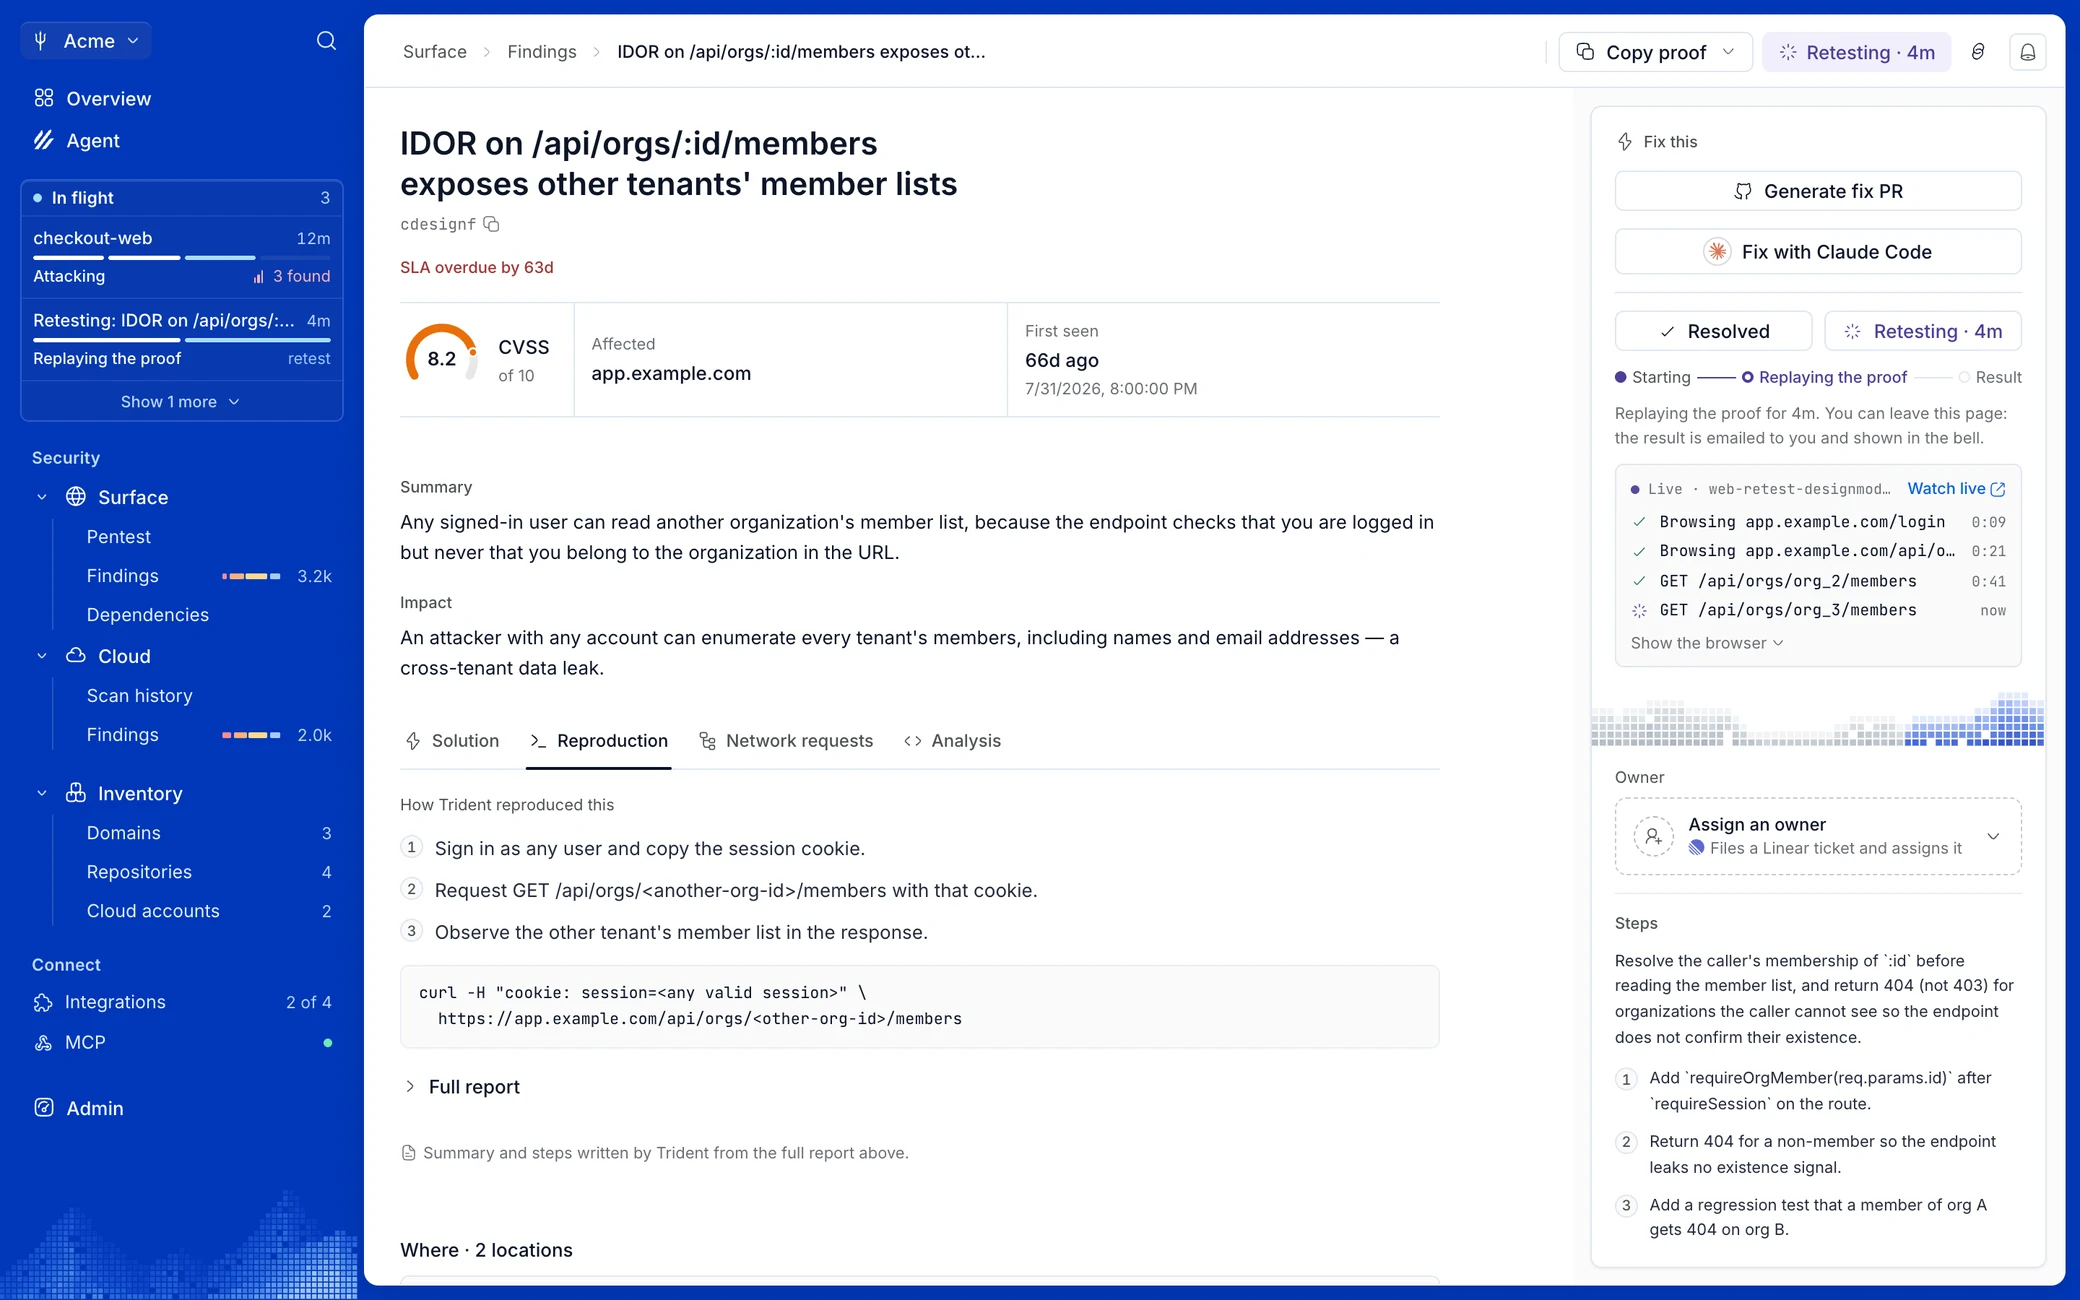
A proven finding in Trident: an IDOR on /api/orgs/:id/members with its CVSS score, how Trident reproduced it, and a live retest replaying the proof

Trusted by teams shipping fast

What Trident does

From the first scan to a merged fix.

01 PENTEST

Pentests that prove every finding.

Trident runs the attack instead of guessing at it. Agents map the app, try each idea against it, and replay every candidate from a clean session. Only what reproduces becomes a finding.
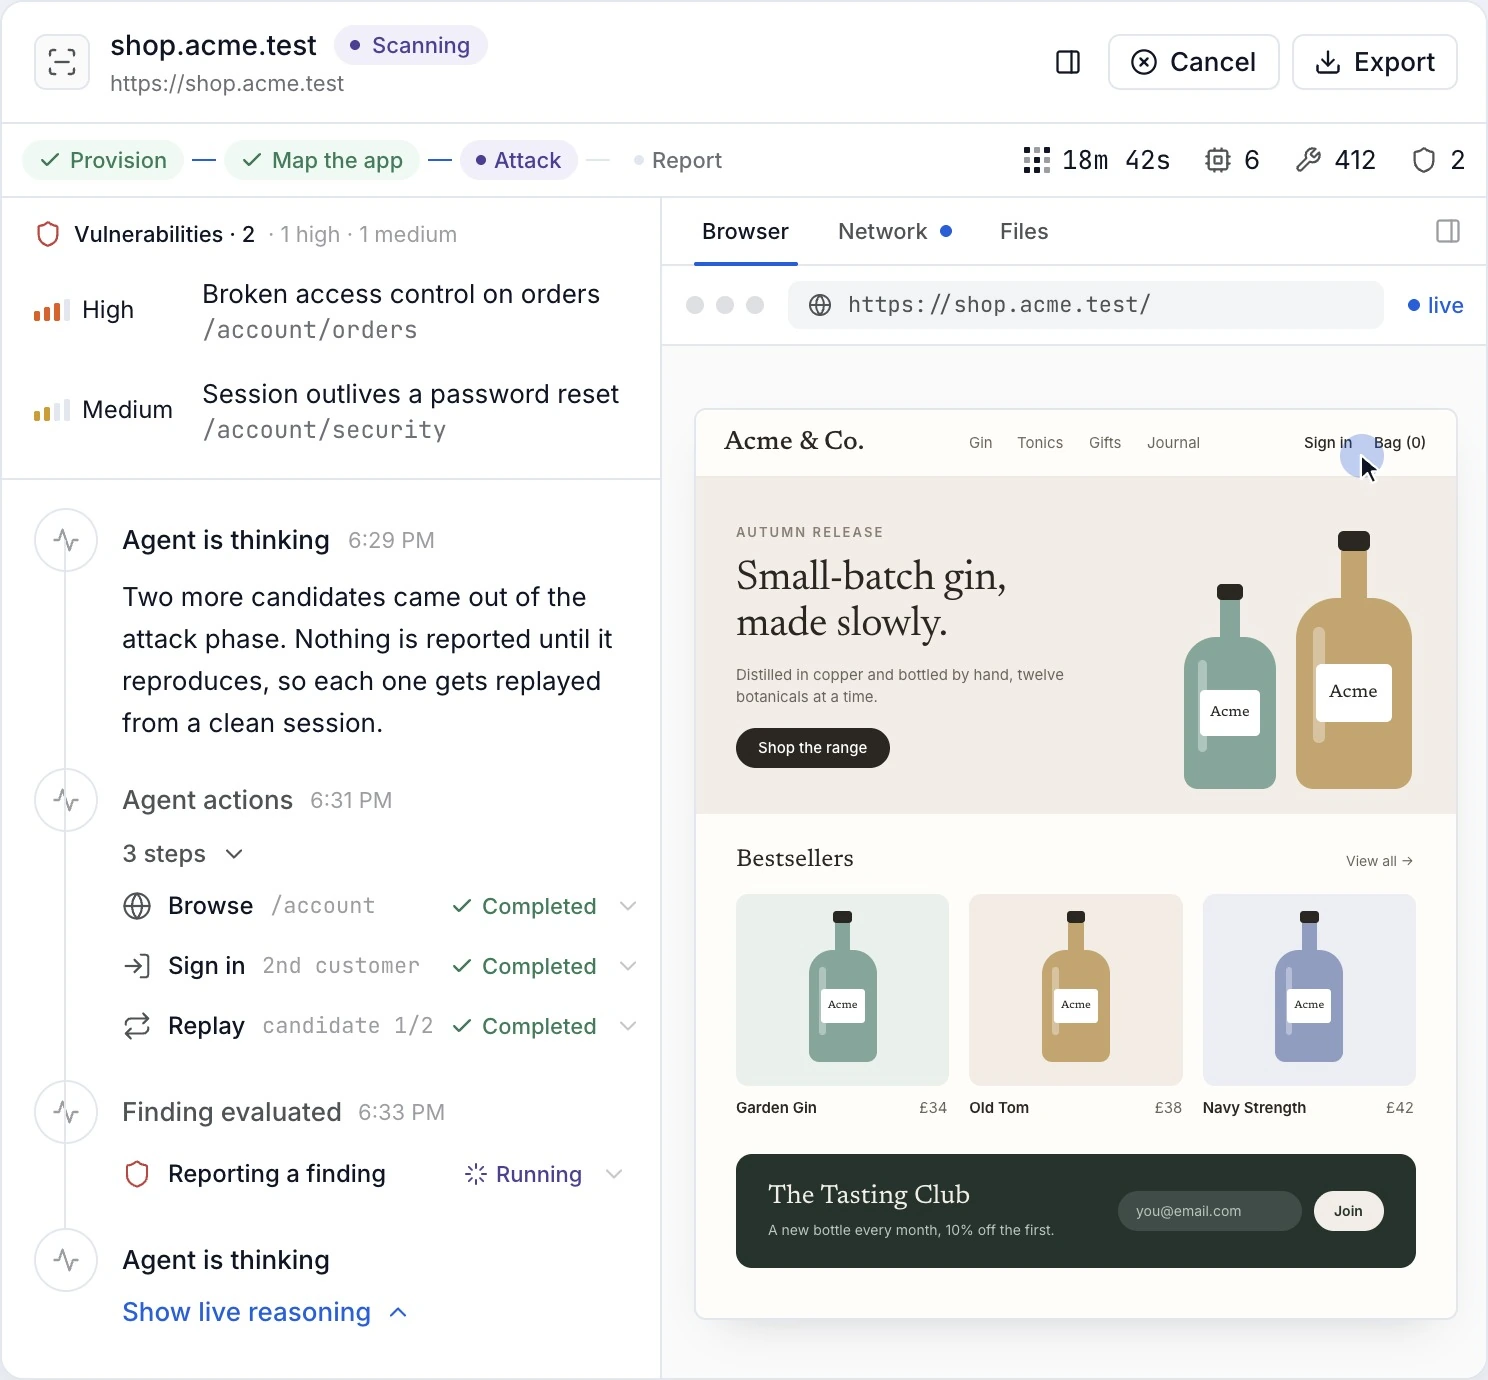
Trident's live scan of shop.acme.test in the Attack phase: two findings so far, the agent replaying each candidate from a clean session before it reports, and the browser it is driving open on the right.
Validated by doing
Every candidate is replayed before it counts. What doesn't reproduce is dropped, not reported.
Proof attached
Each finding carries the steps that reproduce it and a CVSS score.
Watch it work
Follow every agent step live, as it happens.
Retest in one click
After a fix, Trident replays the proof.
See a sample finding
02 PR REVIEW

Caught before it merges.

trident-sentinel reads every change as the PR opens and on each push, flags the exact lines with a fix to commit, and can hold the merge until it is fixed.

Every PR, every push
trident-sentinel reviews the change as the PR opens and again on each push.
The exact lines
Each finding points at the lines it came from, with the reason in plain words.
A fix to commit
The suggested change commits straight from the review.
Holds the merge
Make the check required and nothing ships until it's fixed.
See PR review
03 MCP

Fixes start in your editor.

Your coding agent pulls a finding over MCP, proof of concept included, and patches it where you already write code.

Findings over MCP
Your agent lists open findings and pulls one with its proof of concept.
Patched where you code
Claude Code, Cursor and Copilot make the change in your repo.
Proven before the PR
The proof runs as a test, so the draft PR only opens when it passes.
Plug in your agent
04 SLACK

One mention, a straight answer.

Tag @Trident in any channel and it answers in the thread from your live findings, scans and PR reviews.

Any channel
Mention @Trident wherever the question comes up.
From live data
Answers come from your current findings, scans and PR reviews.
Straight to the proof
Every answer links back to the finding in Trident.
Set up @Trident
FROM THE LOGBOOK

Proof, not promises

Four soundings we take on every account, from the surface to the seabed.

24h
From connecting to the first verified critical finding
SOUNDING 01 · SURFACE
0 M
Every PR
Read like an attacker would, before it merges
SOUNDING 02 · TWILIGHT
200 M
0
Findings sent to you without a proof of concept
SOUNDING 03 · THE DEEP
1,000 M
6 → 1
Scanners merged into one list, ranked by risk
SOUNDING 04 · SEABED
4,000 M

Connect the places an attacker would look first

Read-only, in minutes. Trident maps everything it can reach before the first probe goes out.

See every integration
shop.acme.testWEB APP
acme/payments-apiREPO
aws · 4 accountsCLOUD
  1. 01Map every route
  2. 02Attack like an adversary
  3. 03Prove each finding
  4. 04Draft the fix

One crew, every surface

Notes from the lab

ALL
CAST A LINE

Find it before they do.

Start a free trial. Your first verified findings land within a day of connecting.