The paths thatreach your data.
One graph across AWS, Azure, GCP and Kubernetes. See the attack paths that end at your crown jewels, ranked by what they reach.
 AWS
 Azure
 GCP
 Kubernetes
READ-ONLY CONNECTION · NO AGENTS DEPLOYED
01THE PROBLEM
Paths, not counters.Ranked by what they reach.
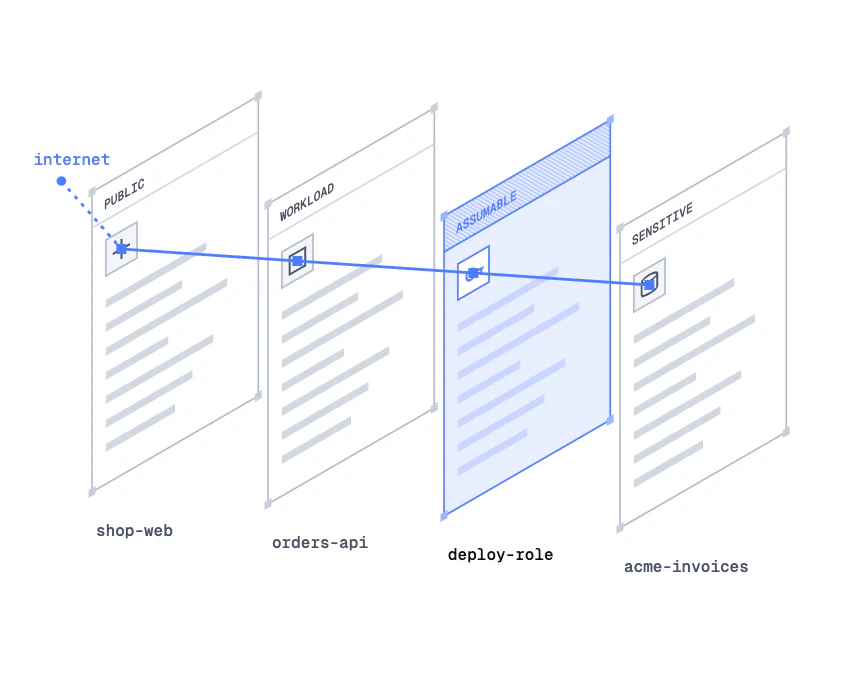
Scanners flag each condition on its own. An attacker chains them. Trident looks at the chain.
- 6to 1Scanners merged into one list, ranked by risk.
- 1 hopEvery path names the one hop that closes it, usually an over-privileged role.
- 0 agentsA read-only connection builds the graph. Nothing is deployed.
Scanners dump thousands of standalone misconfiguration alerts, with no way to tell which reach production data. Trident joins exposure, IAM edges and findings into ordered, multi-hop paths that end at a named data store.
SEE HOW IT WORKS02ONE RANKED LIST
Six scanners in.One ranked list out.
Exposure, IAM and findings correlate into ranked attack paths, so the list starts with what reaches your data.
Alerts in, attack paths out
Standalone alerts from six kinds of scanner, joined into one list ordered by what each path reaches.
Illustrative. Bar heights show alert volume, not measured counts.
03KNOW THE PATH
Know the path.Close the risk.
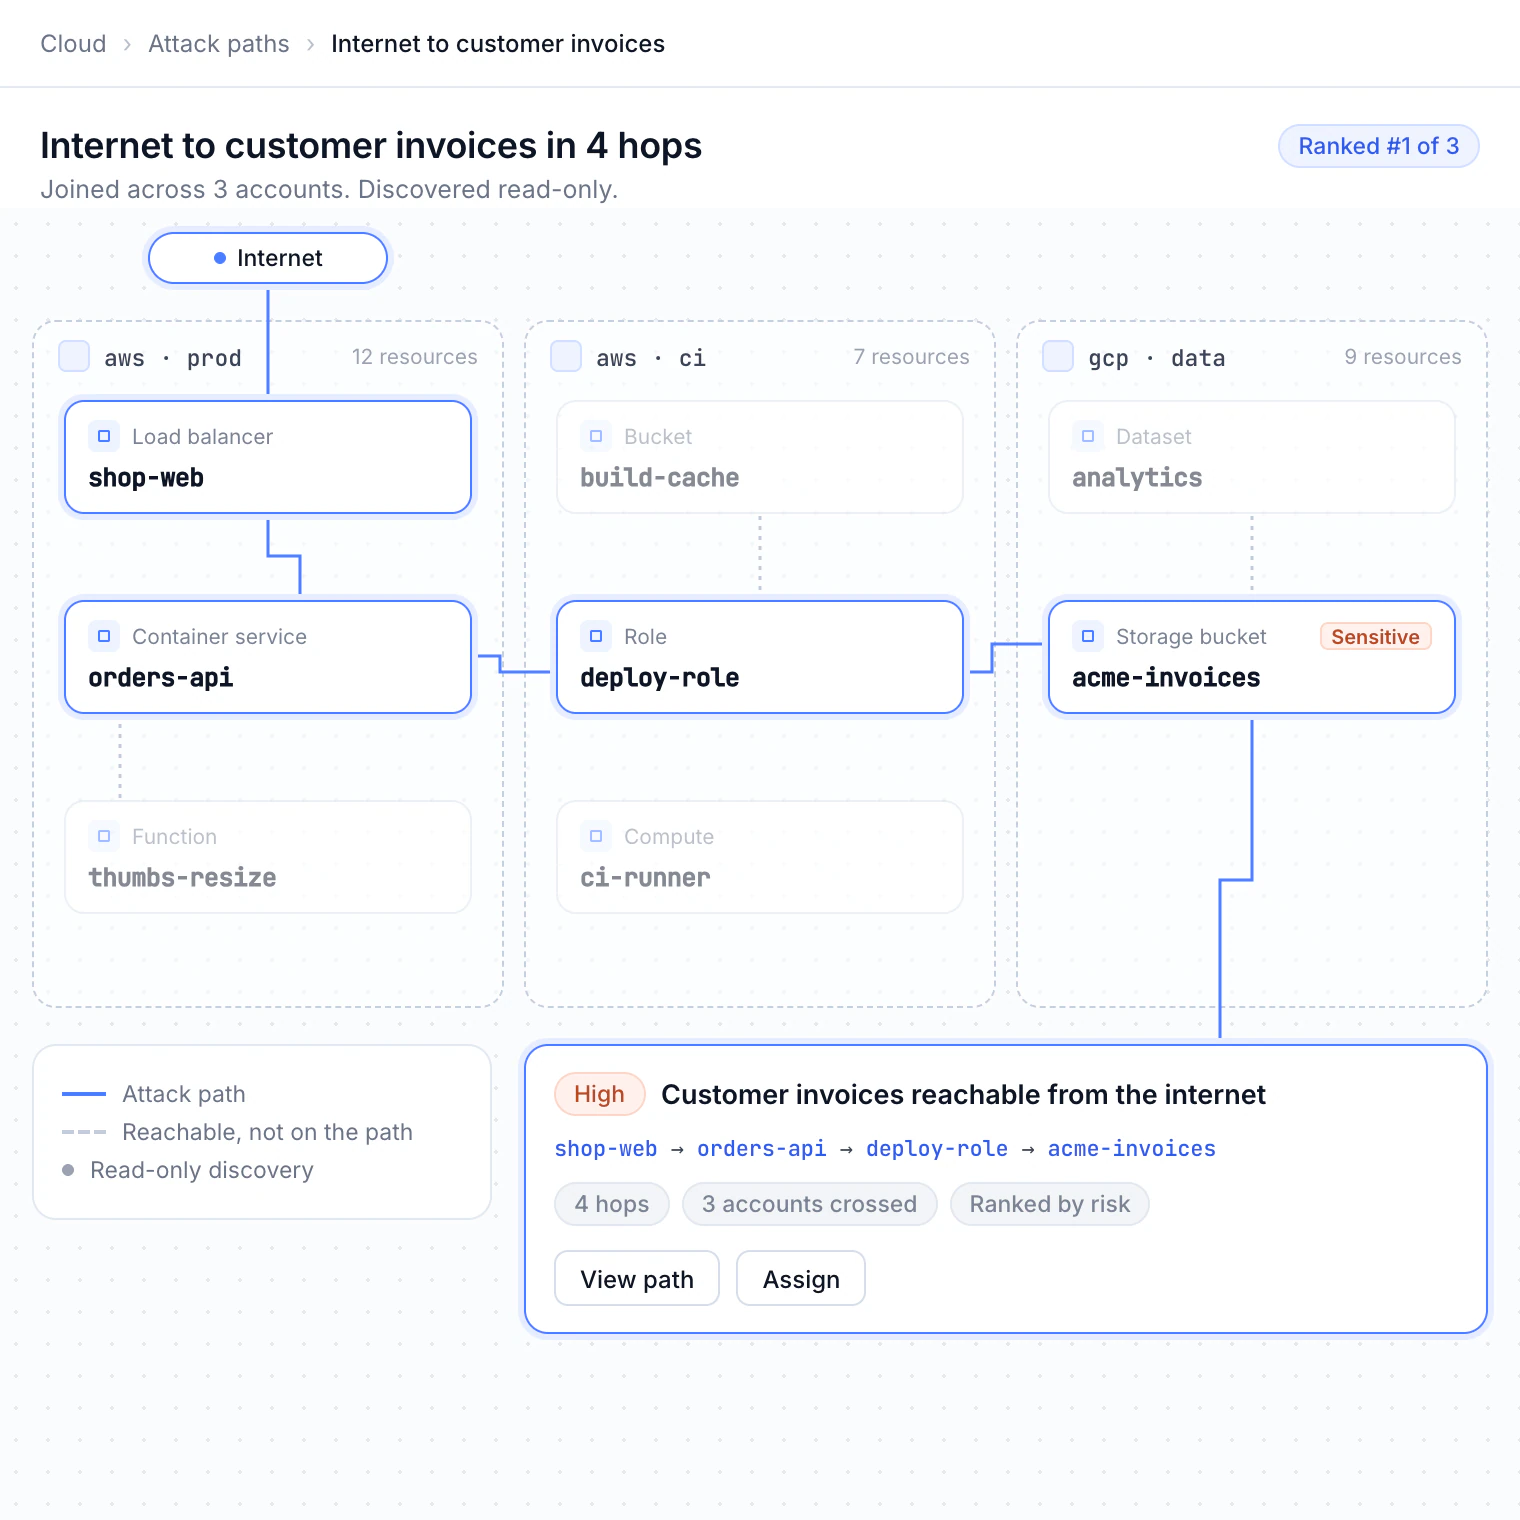
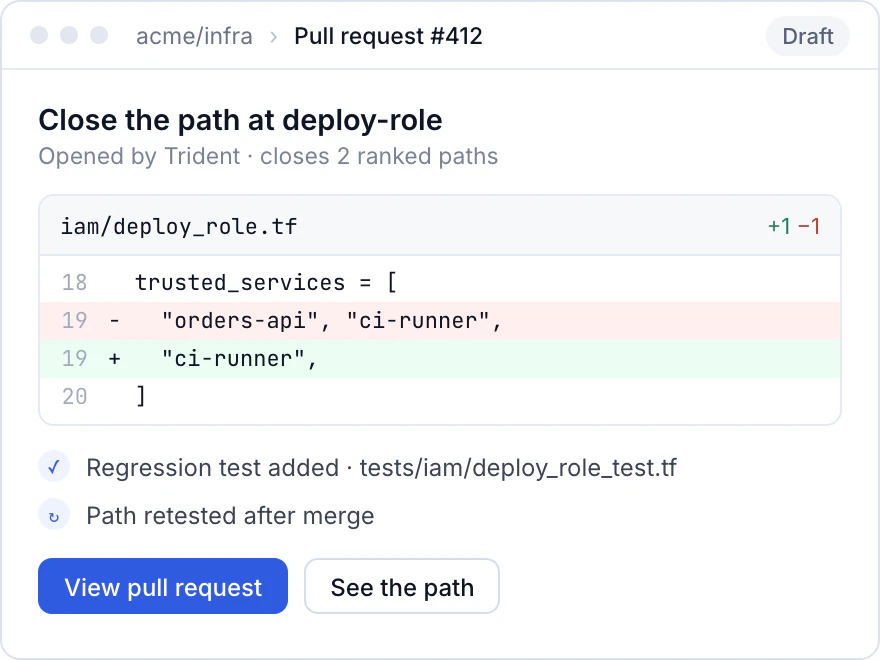
Every path names the one hop that closes it, usually an over-privileged role. Each path opens a draft PR with remediation and a regression test.
Choke-point remediation
Every path names the one hop that closes it, usually an over-privileged role.
Proven, not theoretical
Paths rank by evidence Trident can reproduce, not by configuration noise.
Fixes engineers can merge
Each path opens a draft PR with remediation and a regression test.
04HOW IT WORKS
From read-only roleto a merged fix.
Exposure, identity and scanner findings collapse into ranked paths to crown-jewel data.
Attach a read-only role. Trident inventories assets, identities and data stores across every account.
Assumes-role, reaches, exposes and stores resolve into one graph. Exposure, identity and findings join into paths.
Each path ships its choke-point fix with proof and a test.
05COVERAGE
AWS, Azure, GCPand Kubernetes. One graph.
Inventory every resource and identity, then trace blast radius from any asset. SOC 2, CIS and PCI posture sit on the same graph as the risk.
AWS
Accounts and organizations
READ-ONLY
Azure
Subscriptions
READ-ONLY
GCP
Projects
READ-ONLY
Kubernetes
Clusters
READ-ONLY
- AWS · Azure · GCPCLOUD CONTEXT
- Read-onlyCONNECTION MODEL
- ConnectedASSETS, IDENTITIES AND DATA
- RetestedAFTER REMEDIATION
06QUESTIONS
Frequentlyasked.
An ordered set of reachable relationships that could let an attacker move from an initial foothold to a material target. A path can combine internet exposure, a workload weakness, IAM permissions, trust policies, network reachability and access to sensitive data.
CSPM continuously identifies configuration and posture issues. Attack path analysis connects selected issues with identity, network, workload and data relationships to find which combinations create a route to a critical target. The two complement each other.
A set of individually limited conditions that becomes materially risky when combined, such as public reachability, a vulnerable workload, an assumable role and access to a sensitive data store.
A relationship or control shared by one or more attack paths. Narrowing a role trust policy, reducing a permission or isolating a data store can break several paths with one change.
A read-only role. No agents are deployed.
Find it beforethey do.
Start a free trial. Your first verified findings land within a day of connecting.
- SOC 2 audited by Sensiba LLP
- Read-only cloud access