PRODUCTPR REVIEW
Caught beforeit merges.
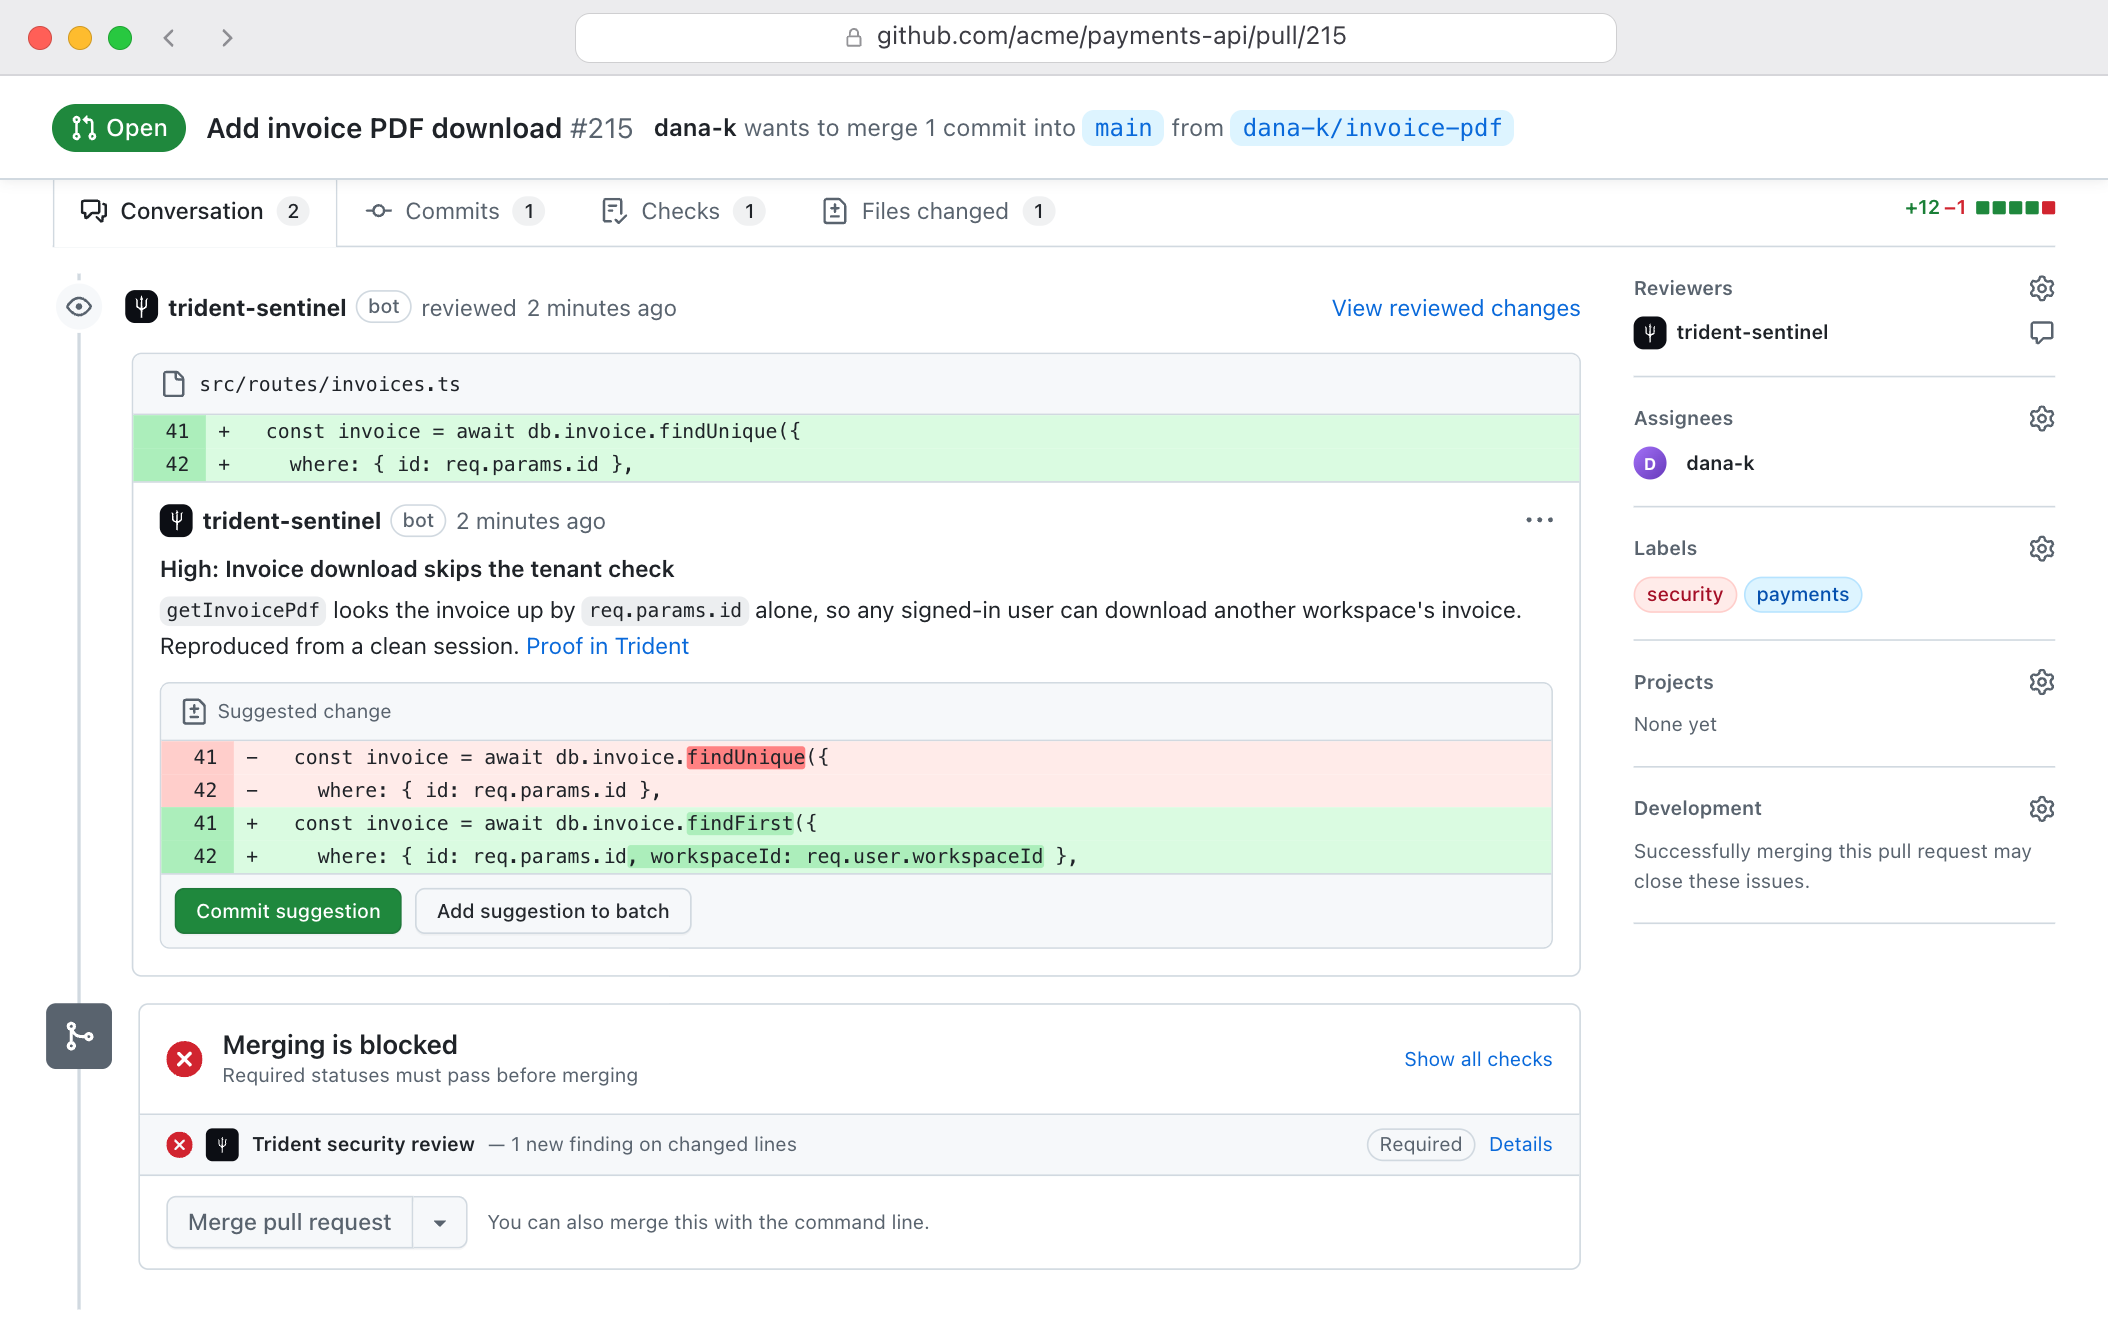
trident-sentinel reads every change as the PR opens and on each push, flags the exact lines with a fix to commit, and can hold the merge until it's fixed.
01HOW IT REVIEWS
Every pull request,read like an attacker.
trident-sentinel reviews the change as the PR opens and again on each push. Each finding points at the exact lines, with a fix you can commit from the review.
acme/billing-api#214 · Add invoice PDF download
- a1f9c2Opened1 high · merge held
- 7be04dPushedFixed on push
- c33e10PushedNo new findings
trident-sentinel reviews the PR as it opens and again on each push.
The exact lines
Each finding points at the lines it came from, with the reason in plain words.
A fix to commit
The suggested change commits straight from the review.
Holds the merge
Make the check required and nothing ships until it's fixed.
GitHub and Bitbucket
A required check and a review on GitHub; a build status and inline comments on Bitbucket.
02ONE PULL REQUEST
One pull request,from flagged to fixed.
dana-k opens #214. trident-sentinel flags line 42 with the reason
and a fix. One commit later the review runs again and the merge opens.
Invoice download skips the tenant check
The invoice is looked up by id alone, so any signed-in user can download another workspace's invoice. Reproduced from a clean session.
View proof in Trident
- on open01
dana-k opens #214
trident-sentinel reviews the change as soon as the PR opens.
- inline · L4202
Line 42, with the reason
The invoice is looked up by id alone. The comment says why and carries the change that fixes it.
- re-checked on push03
Commit, re-check, merge
Commit the suggestion; the review runs again on the push and the required check clears.
03SET UP
Connect it once.Make it required.
Connect GitHub or Bitbucket and every pull request gets a review. Make the check required and nothing ships until it's fixed.
- 01
Connect your repositories
GitHub or Bitbucket.
- 02
Open a pull request
trident-sentinel reviews it as it opens and again on each push.
- 03
Require the check
Add Trident security review to your branch rule. Nothing merges until it passes.
Branch protection rule
Branch name pattern
Require a pull request before merging
When enabled, all commits must be made to a non-protected branch and submitted via a pull request.
Require status checks to pass before merging
Choose which status checks must pass before branches can be merged into a branch that matches this rule.
Require conversation resolution before merging
All conversations on code must be resolved before a pull request can be merged.
SOC 2 report
Audited by Sensiba LLP. Request it from the Trust Center.
04FAQ
Questions,answered.
As the pull request opens and again on each push. Each finding points at the lines it came from, with the reason in plain words.
GitHub and Bitbucket. On GitHub, trident-sentinel comments on the changed lines and reports a check. On Bitbucket, a build status and inline comments.
Yes. The Trident security review check lists new findings on changed lines and clears once they're fixed. Make it required to hold the merge.
Yes. Start a free trial, and your first verified findings land within a day of connecting.
Hold the mergeuntil it’s fixed.
Connect GitHub or Bitbucket and trident-sentinel reviews the next pull request as it opens.
- SOC 2 audited by Sensiba LLP
- GitHub and Bitbucket